Quick Answer
A document verification workflow is a sequence of checks used to evaluate a submitted document. It typically includes document submission, quality checks, data extraction, classification, authenticity and fraud checks, source verification, information matching, manual review when needed, and a final verification decision with supporting records or reports.
What Is a Document Verification Workflow?
A document verification workflow is a structured sequence of checks performed on a submitted document to evaluate its authenticity, integrity, validity and the information it contains.
Why Document Verification Uses Multiple Stages
Reading what a document says is not the same as verifying it. A system can extract every field on a certificate perfectly and still have no idea whether that certificate is genuine. That is why verification runs through several distinct stages rather than treating extraction as the finish line. Each stage answers a different question about the document.
Does Every Document Follow the Same Workflow?
No. Workflow stages vary depending on the document type, the verification objective, what sources are actually available, the risk level involved, the organization’s own requirements, the applicable jurisdiction and whether human review is needed.
NIST’s identity proofing guidance makes a similar distinction, separating the collection of evidence from validating its authenticity, validating the information it contains and verifying the relationship between that evidence and the person presenting it.
The point worth remembering throughout this guide: extraction is not verification.
How Does Document Verification Work?
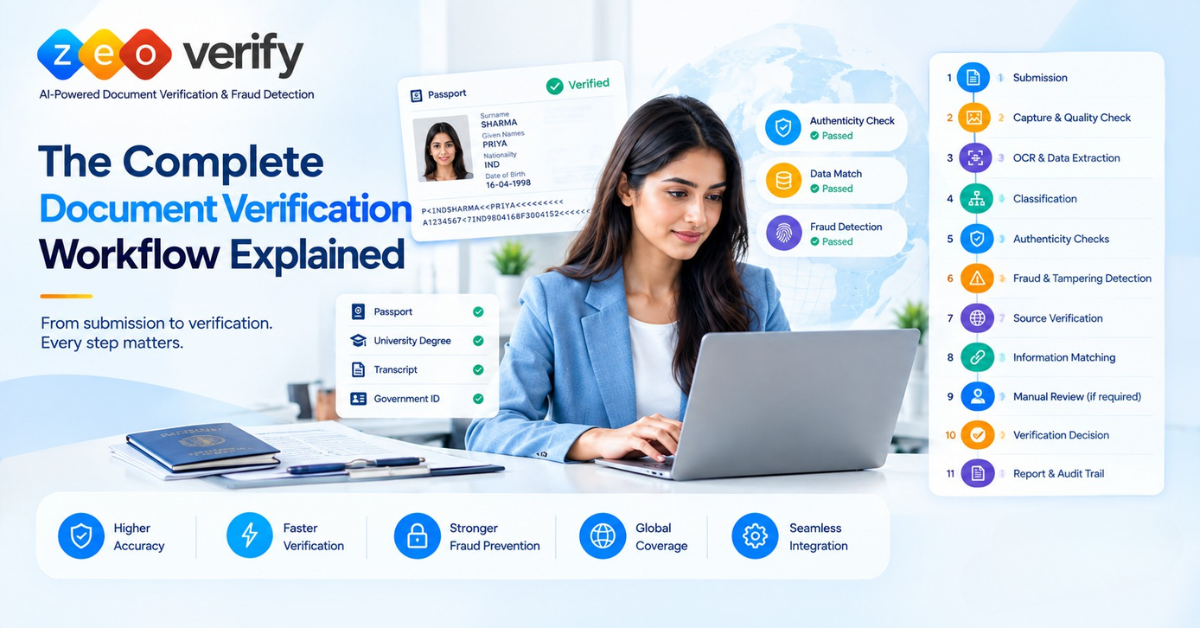
At a high level, a document moves through this sequence:
- Submission
- Capture and quality check
- OCR and data extraction
- Classification
- Authenticity checks
- Fraud and tampering detection
- Source verification
- Information matching
- Manual review if required
- Verification decision
- Report and audit trail
Not every workflow performs every check, and not always in exactly this order. A system verifying a passport for a bank onboarding flow and a system verifying an academic transcript for a university will share the general shape while differing considerably in the specific checks applied.
What Are the Steps in Document Verification?
1. Document Submission
The workflow starts when a user or organization submits the document, which might be a passport, government ID, academic certificate, transcript, financial document or another record depending on the use case.
Submission can happen through a direct upload, a live image capture or a connected source. Both the document type and where it came from influence what happens downstream, since a document retrieved from an official source carries different weight than a photo of a photocopy. This stage is document intake rather than verification itself.
2. Document Capture and Quality Check
Before anything can be analyzed, the system checks whether the document is actually usable, looking at resolution, blur, lighting, orientation, cropping, missing sections, obscured information and overall completeness. Poor quality input prevents reliable downstream analysis, and no amount of clever processing later will fix a document that was half cut off at capture.
There is an important distinction here. The quality check asks “can this document be processed reliably?” The authenticity check, which comes later, asks “does this document appear genuine?”
3. Data Extraction Using OCR
OCR converts the document image into structured, machine readable data:
Document image → OCR → Extracted text and data → Structured fields
Typical extracted fields include name, dates, document number, address, issuing institution and other relevant details depending on the document type.
This is worth stating plainly: OCR extracts information. It does not, by itself, establish that the source document is authentic. OCR will happily read a convincingly forged certificate and hand you perfectly structured data from it. The authenticity question gets answered later in the workflow.
4. Document Classification
The system identifies what kind of document has been submitted, sorting it into a category such as passport, government ID, driver’s license, academic certificate, transcript or financial document.
Classification matters because it determines which fields, formats, rules and checks are actually relevant. You would not apply passport security feature checks to a university transcript.
5. Authenticity and Security Checks
This is where the system evaluates whether the document appears genuine. Checks can include expected structure, document format, security features, required fields, layout, issuer information, metadata where relevant, internal consistency and digital security features where applicable. NIST identifies completeness, format, security features and signs of counterfeit or tampering as relevant elements of evidence validation.
An important caveat: not every document contains the same security features, and not every verification workflow has access to the same validation methods. A modern ePassport offers far more to check against than a scanned certificate from a small institution.
6. Tampering and Fraud Detection
This stage looks for indicators associated with altered or fraudulent documents, including altered fields, image manipulation, inconsistent formatting, suspicious patterns, missing expected elements, forged information and recaptured or manipulated images where detectable. The technology involved can include AI, machine learning, computer vision and rules based analysis.
Worth being precise about what this actually does: automated systems can identify indicators associated with tampering or suspicious documents. They do not independently prove fraud. A flag is a signal that something warrants closer attention, not a verdict.
7. Database or Source Verification
Where possible, extracted information gets checked against a trusted source:
Extracted information → Trusted or authoritative source → Comparison → Result
Potential sources include the issuing organization, a government database, a registry, an institution, an API or another connected source.
Not every document can be checked this way. NIST explicitly notes that validation against an issuing or authoritative source depends on what information is actually available for a particular evidence type. Where source verification is available, it tends to be one of the strongest signals in the whole workflow.
8. Identity and Information Matching
The system compares extracted attributes such as name, date of birth, document number, address and other relevant fields, often checking consistency across multiple submitted documents.
This stage can support identity verification, but it is worth keeping the distinction clear: document verification and identity verification are not automatically the same process. Confirming a document is genuine is different from confirming the person presenting it is its rightful owner.
9. Manual Review, When Required
Automated verification does not always produce the final result on its own. Human review may be triggered by ambiguous results, poor quality evidence, suspicious indicators, missing information, exceptions, higher risk cases or insufficient source evidence. This human in the loop model is not about manual review being better or worse than automation. It is about routing cases that genuinely need judgment to a person while letting the system handle routine volume.
10. Verification Decision and Results
The workflow produces an outcome, which depending on the system might be verified, failed, rejected, needs review or additional information required. Result categories vary by verification provider and organizational workflow. The decision should reflect the combined results of all preceding checks rather than any single OCR or fraud detection signal in isolation.
11. Report and Audit Trail
Finally, the system records what happened, which can include the verification outcome, which checks were performed, timestamps, review history, relevant evidence, exceptions and supporting information. Not every system stores every item, but a solid audit trail is what makes a verification defensible later if anyone asks how a decision was reached.
Example of a Document Verification Workflow: Academic Certificate
Here is how the sequence plays out for a single realistic document.
An academic certificate is submitted, then quality checked for readability. Information is extracted, the document is classified as an academic certificate, and authenticity indicators are checked against expected formats for that document type. Tampering indicators are analyzed, source verification is performed where the issuing institution can be reached, and extracted information is matched against other submitted records. If anything is ambiguous, the case routes to manual review. A verification decision follows, along with a verification report and audit record.
The exact checks depend on the certificate type, the issuing institution, available verification sources and the organization’s verification policy.
What Technologies Are Used in Document Verification?
| Technology | Role in Workflow | Example |
|---|---|---|
| OCR | Extracts text and fields | Reading names and document numbers |
| AI and machine learning | Identifies patterns and anomalies | Flagging suspicious characteristics |
| Computer vision | Analyzes visual document characteristics | Detecting potential image manipulation |
| Rules based validation | Checks defined conditions | Checking required fields or formats |
| Source verification | Compares information with trusted sources | Checking issuer information |
| APIs and integrations | Connects verification to external systems | Sending results to an organization’s workflow |
Not every verification system uses all of these. They are components that may support different workflow stages depending on how the platform is built and what the organization needs.
Manual vs Automated Document Verification
| Factor | Manual | Automated |
|---|---|---|
| Data extraction | Human led | Technology assisted |
| Processing | Human dependent | System driven |
| Scalability | More operational effort at volume | Designed for higher volume workflows |
| Consistency | Depends on reviewer and process | Rules and system checks standardize processing |
| Human involvement | High | Often focused on exceptions |
| Exception handling | Direct human assessment | Routes flagged cases for review |
Neither approach is universally better. Most organizations processing meaningful volume end up with a hybrid, where automation handles the routine cases and humans handle the exceptions.
What Happens When Document Verification Fails?
Common Reasons for Failure
- Poor image quality
- Missing information
- Inconsistent information
- Unsupported document type
- Suspected tampering
- Information mismatch across documents
- Unable to verify against an available source
- Expired document where relevant
- Technical processing issue
A failed verification result does not automatically mean fraud. Often it simply means the system could not establish sufficient evidence for a successful verification result. A genuinely valid certificate photographed badly in poor lighting can fail just as easily as a forged one.
What Happens Next?
The usual flow looks like this:
Failure or flag → Reason identified → Review or correction → Resubmission or additional evidence → Final decision
Most failures are recoverable. The user resubmits a clearer image, provides a missing document or clarifies an inconsistency, and the workflow runs again.
How Long Does Document Verification Take?
There is no universal processing time. Duration depends on the document type, image quality, the verification method used, how much is automated, whether authoritative sources are available and responsive, how many documents are involved, whether manual review is triggered and the organization’s own workflow. Automated checks on a clean, well supported document can complete quickly, while a case routed to manual review with limited source availability takes considerably longer.
Is Automated Document Verification Secure?
Automated verification systems can include encryption, authentication, access controls, secure data handling, audit trails, tamper detection, data minimization and controls aligned with applicable privacy and security requirements.
That said, security depends on system design, implementation, configuration, access controls, data handling practices and the organization’s own procedures. No verification system should be described as completely secure or fraud proof. What matters is asking specific questions about how a given platform actually handles your data.
How ZeoVerify Streamlines the Document Verification Workflow
ZeoVerify approaches this as a connected workflow rather than a collection of separate checks: document input, verification workflow, fraud prevention, verification result and report. The platform offers AI powered document verification with fraud detection capabilities, secure verification workflows, secure authentication, encryption and verification reports through a user friendly interface.
One workflow worth highlighting is DigiLocker based verification. Where applicable, ZeoVerify can retrieve documents directly through DigiLocker after user authentication and consent, rather than relying on a manually uploaded or scanned copy. That changes the starting point of the workflow meaningfully, since the document arrives from an official source rather than as an image someone captured on a phone.
Talk to the ZeoVerify team to explore how automated document verification can fit into your organization’s verification workflow.
Key Takeaways
- Document verification is a multi stage process, not a single check
- Submission and data extraction are only the beginning
- OCR extracts information but does not independently prove authenticity
- Authenticity and fraud checks evaluate the document itself
- Source verification strengthens validation where authoritative sources are available
- Some cases require manual review
- Final results should be supported by appropriate records or reports
Workflow recap: Submission → Quality check → OCR → Classification → Authenticity → Fraud detection → Source verification → Matching → Review → Decision → Reporting
Frequently Asked Questions
What is a document verification workflow?
It is a structured sequence of checks performed on a submitted document, covering submission, quality, extraction, classification, authenticity, fraud detection, source verification, matching, review and a final decision.
How does OCR help with document verification?
OCR converts the document image into structured data the rest of the workflow can analyze. It extracts information but does not establish whether the document is genuine.
Can document verification detect tampered documents?
Systems can identify indicators associated with tampering, such as altered fields or inconsistent formatting. These are signals for review rather than definitive proof.
What is the difference between document verification and document authentication?
Document verification is the broader evaluation of a document’s authenticity, integrity, validity and information. Authentication focuses more narrowly on whether the document is genuine or from a legitimate source.
Why does document verification fail?
Common reasons include poor image quality, missing or inconsistent information, unsupported document types, suspected tampering or an inability to verify against an available source.